Privacy & Security

Agents That Follow Your Rules,
in an Environment You Control

Kizen powers mission-critical moments for regulated enterprises. Every agent runs under the same permission model as your people, on the models and infrastructure you choose, with controls that are independently audited.
Your data, our responsibility

Built Security-First for Enterprise Trust
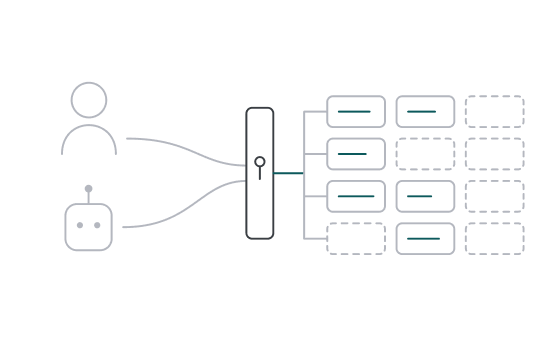
Least-Privilege Agents

Every Kizen agent works under the same field-level permissions as your people, through the same governed API and MCP, so it can never see or do more than you’ve allowed.
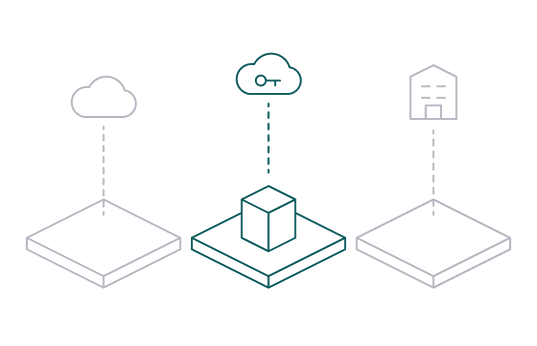
Control Where Data Lives

You own your data and decide where it runs: Kizen’s cloud, your cloud or on-premises, on the models you approve, with your own API keys.

Your data is encrypted in transit and at rest using industry-standard algorithms.
Verifiable Assurance

Kizen is independently audited against ISO 27001, SOC 2 Type II and HIPAA, with a complete audit trail of every action people and agents take.
Control and Oversight by People

Escalate decisions that require a person’s approval, so licensed staff stay accountable for regulated outcomes while agents handle the work around them.

Certified To The Standards You’re Held To

Information Security & Certifications

Enterprises rely on Kizen to run agents inside their most sensitive workflows, so we build every part of the platform to be secure, reliable, observable and scalable. Kizen holds ISO 27001 certification and a SOC 2 Type II certification, and is HIPAA compliant.

Our information security management system (ISMS) follows ISO/IEC 27001 and is overseen directly by top leadership at Kizen. We assess risk at every level, from company objectives to individual product changes. Our controls are reviewed every year, audited independently, and tested through annual third-party penetration testing.

For reports, policies and our full list of controls, visit our Trust Center.

Certification Overview

Service Organization Control (SOC):
  • SOC 2, Type 2 (Security, Confidentiality, and Availability)
International Organization for Standardization (ISO)
  • ISO27001:2022
Additional
Verifications
  • AWS FTR
  • Google CASA Tier 2
  • CSA STAR Level 1

Kizen is HIPAA compliant and signs business associate agreements with healthcare customers and with the AI model providers we use to process their data. Beyond our own certifications, Kizen is built for regulated industries. Field-level permissions, human approval steps and a full audit trail of every action people and agents take can be configured to help customers meet requirements such as those arising from:

  • HIPAA (Health Insurance Portability and Accountability Act)
  • Fair lending and adverse action notice requirements (ECOA / Regulation B)
  • NAIC Model Bulletin on insurers’ use of AI
  • State laws requiring licensed professionals to make coverage and medical-necessity decisions
  • State privacy laws such as the CCPA

HIPAA Anti-Retaliation Policy

Title II of the Federal Health Insurance Portability and Accountability Act (42 USC 1320d to 1329d-8, and Section 264 of Public Law 104191), and its accompanying Privacy Regulations, 45 CFR Parts 160 and 164, require that “covered entities,” as defined by the HIPAA Privacy Regulations, refrain from any retaliatory acts targeted toward those who file complaints or otherwise report HIPAA violations or infractions. The purpose of this policy is to clearly state the position of Kizen on intimidation and retaliation. This policy applies to all workforce, volunteers, and management of Kizen.

Under no circumstances shall Kizen intimidate, threaten, coerce, discriminate against, or take other retaliatory action against any individual for:

  • The exercise of rights guaranteed under HIPAA, including the filing of a HIPAA complaint against Kizen;

  • The filing of a HIPAA complaint with the Secretary of HHS;

  • Testifying, assisting, or participating in a HIPAA investigation, compliance, review, proceeding, or hearing; or

  • Opposing any act or practice that is counter to the HIPAA regulations, provided the individual or person has a good faith belief that the practice opposed is unlawful, and the manner of the opposition is reasonable and does not involve a disclosure of PHI in violation of HIPAA.

  • No retaliatory action against an individual or group involved in filing HIPAA complaints or otherwise reporting infractions will be tolerated. Under no circumstances shall Kizen require any member(s) of its workforce, volunteers, or management to waive their rights under HIPAA. All allegations of HIPAA retaliation against individuals will be reviewed and investigated by Kizen in a timely manner.

Responsible Disclosure Policy

Disclosure policy

  • If you believe you’ve discovered a potential vulnerability, please let us know by emailing us at security@kizen.com. We will acknowledge your email promptly.

  • Provide us with a reasonable amount of time to resolve the issue before disclosing it to the public or a third party.

  • Make a good faith effort to avoid violating privacy, destroying data, or interrupting or degrading the Kizen service.

  • Please only interact with accounts you own or for which you have explicit permission from the account holder.

Exclusions

  • While researching, we’d like you to refrain from:

  • Distributed Denial of Service (DDoS)

  • Spamming

  • Social engineering or phishing of Kizen employees or contractors

  • Any attacks against Kizen’s physical property or data centers

  • Thank you for helping to keep Kizen and our users safe!

Additional Security & Services

Confidentiality and Sensitive Information

Kizen will follow industry best practices and strict procedures to keep client data, passwords, processes, and other sensitive information secure throughout and after our work together. If desired, the Client may request Kizen delete all sensitive information from the Company’s servers upon termination.

Scope

Kizen will provide software and services as outlined in the provided proposal. If the Client requests training, support, or additional work that falls outside of the scope of the proposal, Kizen will provide an additional proposal or may suggest an hourly based structure to maximize flexibility.

Timelines & Communication

Our mission is to help your business grow as quickly as possible. We bring a sense of urgency to every project and do everything possible to deliver on-time or early. Our projects typically require excellent collaboration between our team and yours. To ensure projects are delivered on-time, please communicate information to our team as quickly as possible and ensure that the information we’re receiving is accurate. Kizen is not responsible for delays caused by the Client, and reserves the right to request additional compensation if inaccurate or delayed information requires additional work to be done.

Copyrights, Trademarks, & Intellectual Property

All data input and generated by the Kizen Platform is owned by the Client. Client guarantees that all elements of text, images, or other artwork provided to Kizen are either owned by the client or the client has written permission to use. When engaging Kizen Services, copyright and intellectual property rights for the work will automatically and permanently be transferred to the client once the final payment for a given project has cleared.

Project Minimum Terms, Cancellation or Suspension

There is no minimum term or cancellation penalty for the Kizen Platform. Client may cancel at any time. Certain Kizen Services have minimum engagement terms as they require significant up-front investments by our team. These items are clearly noted on project proposals. If services are canceled or suspended by Kizen for any reason, the client will receive a full refund. If services are canceled or suspended by the client for any reason, the full amount of services agreed upon will still be due.

Payments

Payment terms are clearly outlined on your proposal. All Kizen invoices are provided digitally. Kizen requests payment via direct deposit, bank wire, or credit card. Payments not received by the due date will result in work cessation. Monthly late charges of $50+10% of the late balance will be added to unpaid balances every 30 days.

Agreement, Invalidity, & Governing Law

This agreement constitutes the entire agreement between Kizen and the client. In the event any individual provision is deemed illegal or unenforceable it shall not affect the validity or enforceability of the remaining provisions. This agreement shall be construed in accordance with the laws of the state of Texas.

Additional Provisions

The terms and conditions of this agreement may be modified or amended as necessary if agreed upon in writing by both parties.

Privacy & Security Q+A

Does Kizen use our data to train AI models?

No.

Is protected health information covered when it's sent to model providers?

Yes. Kizen has BAA's in place with Gemini, Anthropic, and Open AI, which can be accessed directly with your own keys or through Kizen AI. If you bring your own API keys, your own agreement with that provider applies.

Which model providers does Kizen support?

OpenAI, Anthropic, Google Gemini, Mistral AI, Bedrock, Microsoft Foundry and others. We also support OpenRouter for additional models, which are evaluated upon request. You choose which ones your agents use for every LLM step in a workflow.

Can we use our own API keys?

Yes, and our observability still applies. We still provide reporting for usage even if you bring your own key.

Can an agent act without a person's approval?

Only within the explicit permissions you grant. You can require a person to approve specific steps or actions before agents proceed.

How do agents authenticate to our other systems?

Either under the agent's own identity and scoped permissions, or for a specific person through credentials Kizen manages.

Can we run Kizen in our own environment?

Yes. Kizen runs on any major cloud or on-premises.

What happens to our data if we leave?

We delete it from the application under our documented retention and disposal procedures.

Who owns our data?

You do. You own all data you put into Kizen, and any changes made to that data, as well as data created by your team from within Kizen.

How will we hear about a security incident?

Incidents are logged, tracked, resolved and communicated to affected customers under our incident response policy. That plan is tested every year in a table top exercise.

Is my data safe from other Kizen users?

Yes, all data is segregated by strong request-scoped permissions. Segmentation security is part of regular pen-testing.

I see you accept payments. Are you PCI compliant? We have a secure payment gateway integration, but we do not store sensitive credit card data in Kizen.

Do you log data access for HIPAA? Yes, all data access is logged and available upon request.

Can we see your SOC 2 report?

Yes. You can request it through our Trust Center.

How do we report a vulnerability?